
For years, network security was largely built around a simple idea: keep threats outside and trusted users and systems inside. That model becomes harder to maintain when employees work from anywhere, applications and workloads span multiple cloud environments, and third parties, IoT devices, and OT systems connect to the same business infrastructure.
The challenge is no longer limited to stopping unauthorized traffic at the network perimeter. Security teams also need to understand who is accessing a resource, whether the device can be trusted, what systems that access can reach, and whether an attacker who gets in can move further across the environment.
This has turned network security into a broader discipline that brings together firewalls, access controls, network segmentation, threat detection, continuous monitoring, and Zero Trust approaches. The goal is not simply to block attacks at the edge, but to maintain visibility and control across an increasingly distributed network.
This guide explores what network security means today, the solutions and threats organizations need to understand, how Zero Trust and SASE are changing network security architecture, and the best practices for building a more resilient network security strategy in 2026.
Key takeaways
- Network security goes beyond the perimeter. Cloud environments, remote users, third-party connections, and IoT/OT systems have expanded the network organizations need to secure.
- No single security control is enough. Firewalls, access controls, segmentation, monitoring, and threat detection need to work together to address different attack paths.
- Network security needs to be continuously monitored. Detecting unusual activity early can help organizations contain threats before attackers move further through the environment.
- Zero Trust changes how access is managed. Instead of trusting users or devices based on network location, access is verified and limited according to identity, device status, and required permissions.
- Segmentation can limit the impact of a breach. Separating critical systems and workloads makes it harder for attackers to move laterally after gaining initial access.
- Security architecture must evolve with the network. SASE, ZTNA, cloud security, and integrated monitoring are becoming increasingly relevant as organizations move away from traditional perimeter-based environments.
- Compliance and security should be managed together. Network controls should support both day-to-day security operations and the specific requirements that apply to the organization.
What is network security?
Network security is the practice of protecting a network from unauthorized access and activity. It combines security technologies, processes, and policies to control access, protect data, and keep connected systems available.
A useful way to understand network security is through the CIA triad:
- Confidentiality: Prevent unauthorized people from accessing information.
- Integrity: Prevent information from being changed without authorization.
- Availability: Keep systems and data accessible when they are needed.
A stolen database is a confidentiality problem because unauthorized users gained access to the data. An attacker changing records creates an integrity problem, while a DDoS attack that takes a service offline affects availability.
The scope of network security has also expanded beyond the traditional corporate network. Remote employees, cloud workloads, third-party connections, IoT devices, and OT systems can all connect to business environments, giving security teams more access points to monitor and control.
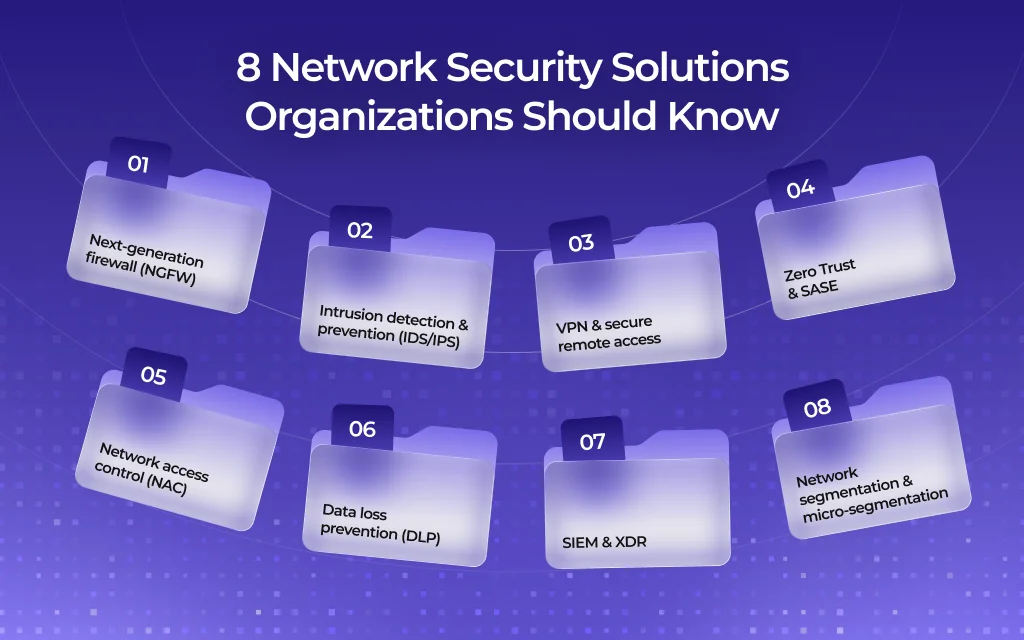
8 types of network security solutions
A network can be attacked at several points, from an exposed internet-facing service to a compromised employee device or an unauthorized connection to a critical system. Different security controls address different parts of this problem, so organizations typically build network security as a combination of traffic filtering, access control, threat detection, data protection, and containment.
The right combination depends on the organization’s environment. A business with remote employees may prioritize secure remote access and Zero Trust, while an organization with sensitive databases or OT systems may place greater emphasis on segmentation and access control.
The following 8 solutions form common layers of an enterprise network security architecture.
1. Next-generation firewall (NGFW)
A next-generation firewall sits at key points in the network and controls which traffic is allowed to pass between networks, systems, and the internet. Unlike traditional firewalls that primarily filter traffic based on IP addresses and ports, NGFWs can identify applications, inspect traffic for threats, and apply more detailed security policies.
This makes the firewall useful for controlling both what can connect and what that connection is allowed to do.
Example: An organization can allow employees to access approved business applications while blocking traffic from a known malicious destination or an unauthorized application.
2. Intrusion detection and prevention (IDS/IPS)
IDS and IPS are designed to identify network activity that may indicate an attack. An IDS monitors traffic and alerts security teams when it detects suspicious patterns, while an IPS can take action to block or stop the detected activity.
These controls add another layer beyond basic traffic filtering because they look for behavior associated with known attack techniques and suspicious network activity.
Example: If an attacker sends repeated exploit attempts toward a vulnerable server, an IPS can detect the malicious pattern and block the traffic before the attack succeeds.
3. VPN and secure remote access
Remote users need a secure way to connect to business resources without exposing sensitive traffic or services directly to the internet. A VPN creates an encrypted connection between the user or remote site and the organization’s network, helping protect data while it is being transmitted.
Traditional VPNs often provide broad network-level access once a user connects. For environments with many remote users and cloud applications, organizations may instead use more granular approaches such as Zero Trust Network Access (ZTNA).
Example: A remote employee can securely connect to internal resources through a VPN, while a ZTNA solution can limit that employee’s access to only the specific applications required for their role.
4. Zero Trust and SASE
Traditional network security often relied on a perimeter: users and devices inside the corporate network were generally considered more trustworthy than those outside it. Zero Trust takes a different approach by requiring access to be verified based on factors such as identity, device status, and the resource being requested.
SASE extends this model to distributed environments by combining networking with cloud-delivered security services such as ZTNA, secure web gateways, and cloud access security controls.
Example: Instead of giving a remote employee broad access after connecting to the corporate network, Zero Trust can verify the employee and device before allowing access only to the applications required for their role.
5. Network access control (NAC)
Network Access Control determines which devices are allowed to connect to a network and what level of access they should receive. Before granting access, NAC can check whether a device is known, authorized, and compliant with security requirements.
This is particularly useful when organizations have many different types of devices connecting to the same environment, including employee endpoints, contractors’ devices, IoT equipment, and other unmanaged systems.
Example: An employee’s laptop may receive normal network access, while an unknown device is denied access or placed into a restricted network until it can be verified.
6. Data loss prevention (DLP)
Network security is not only about stopping attackers from entering the environment. Organizations also need to prevent sensitive information from leaving through unauthorized channels.
DLP monitors the movement of sensitive data and can apply policies when information is being transferred through email, web traffic, cloud services, or other channels. Depending on the policy, it can alert security teams or block the transfer.
Example: If an employee attempts to upload a file containing sensitive customer information to an unauthorized external service, a DLP control can detect the data and prevent the transfer.
7. SIEM and XDR
Security teams need visibility into what is happening across the network to identify attacks that individual security controls may not detect on their own. SIEM collects and correlates logs from network devices, applications, endpoints, and other systems, while XDR connects security telemetry across areas such as network, endpoint, cloud, and identity.
The value comes from connecting these signals. An unusual network connection may not mean much on its own, but it becomes more significant when combined with a suspicious login and unusual activity on the affected device.
Example: A security team can correlate a suspicious login, an unusual network connection, and abnormal endpoint behavior to investigate whether an account or device has been compromised.
8. Network segmentation and micro-segmentation
Network segmentation divides an environment into separate security zones and controls the traffic allowed between them. The purpose is to prevent an attacker who compromises one system from freely reaching other parts of the network.
Micro-segmentation applies this principle at a more granular level, such as individual applications, workloads, or systems. This can be especially important for environments containing critical applications, sensitive data, or OT infrastructure.
Example: If an employee workstation is compromised, network segmentation can prevent the attacker from using that device to directly access a database server or critical OT system.
Top network security threats in 2026
Network threats are becoming more difficult to contain as attackers gain faster access to new techniques and organizations connect more systems to their networks. Cloud environments, third-party access, remote users, and IoT and OT devices have also expanded the number of paths that attackers can use.
The most important threats are not limited to attacks that break through the network perimeter. A compromised account, trusted vendor connection, or vulnerable connected device can give attackers a starting point inside the environment, making detection and containment just as important as prevention.
1. Ransomware and lateral movement
Ransomware attacks can cause more damage when attackers move from the initially compromised system to other parts of the network. Once inside, attackers may attempt to escalate privileges, access critical systems, and disrupt multiple services before deploying ransomware.
What organizations should focus on:
- Network segmentation to limit lateral movement
- Strong access controls and least privilege
- Monitoring for unusual internal traffic
- Tested incident response procedures
2. DDoS attacks
Distributed denial-of-service (DDoS) attacks overwhelm a service or network with large volumes of traffic, making legitimate services difficult or impossible to access. The challenge is not only the size of an attack, but also its ability to create sustained pressure on internet-facing infrastructure.
What organizations should focus on:
- DDoS protection at the network edge
- Traffic filtering and rate limiting
- Redundant network capacity
- Continuous monitoring of traffic patterns
3. AI-powered attacks
AI is changing how attackers conduct reconnaissance, identify vulnerabilities, generate malicious content, and automate parts of an attack. This can reduce the time between discovering a weakness and attempting to exploit it, giving security teams less time to detect and respond.
What organizations should focus on:
- Behavioral threat detection
- Continuous vulnerability monitoring
- Identity and access controls
- Faster detection and response workflows
4. Supply chain and third-party network risk
Third-party connections can create network access that security teams do not fully control. Vendors, service providers, and partners may have legitimate access to internal systems, but a compromised third party can turn that trusted connection into another route into the organization.
What organizations should focus on:
- Limit third-party access to only what is required
- Use dedicated network zones for external parties
- Apply privileged access controls
- Monitor third-party activity and connections
5. OT and IoT network convergence
IoT devices and operational technology are increasingly connected to enterprise networks, creating new paths between traditionally separate environments. Many of these systems were designed primarily for availability and operational requirements, which can make security controls and updates more difficult to implement.
What organizations should focus on:
- Maintain an inventory of connected devices
- Separate IT, IoT, and OT environments where appropriate
- Monitor network traffic between environments
- Apply controls designed for OT-specific protocols and systems
6. Insider threats and credential compromise
A network can be compromised without an attacker directly breaking through a technical control. Stolen credentials, phishing, social engineering, and compromised accounts can give attackers legitimate-looking access that is harder to distinguish from normal user activity.
What organizations should focus on:
- Phishing-resistant MFA for high-risk accounts
- Least-privilege access
- Privileged access management
- Behavioral monitoring for unusual account activity
Zero Trust and SASE in modern network security
Traditional network security was built around a secure internal network and an untrusted internet. That model becomes harder to maintain when employees work remotely, applications move to the cloud, and third parties need access to business systems.
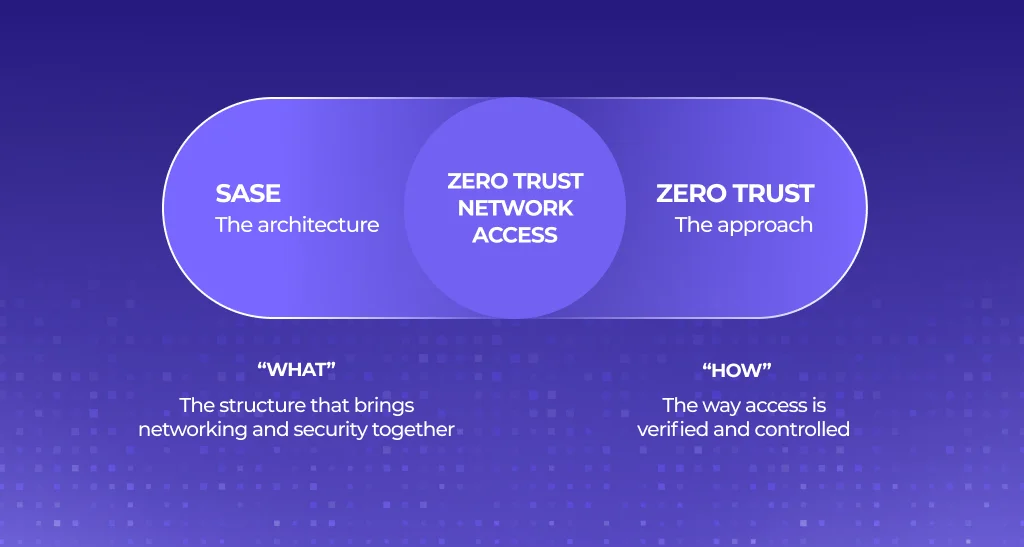
Zero Trust and SASE address this challenge from different but connected angles. Zero Trust defines how access should be secured, while SASE provides the architecture for delivering networking and security services across distributed environments.
Zero Trust: the approach
Zero Trust is a security approach built on the idea that no user or device should be trusted automatically. Every access request should be evaluated based on factors such as identity, device status, context, and the resource being requested.
Its core principles are:
- Verify explicitly: Check the user, device, and access request.
- Use least privilege: Give only the access required.
- Assume breach: Limit the impact if an account or device is compromised.
In other words, Zero Trust defines how access decisions should be made. It moves security away from simply trusting users because they are inside the corporate network.
SASE: the architecture
SASE, or Secure Access Service Edge, is an architecture that brings networking and security capabilities together through cloud-based services. It is designed for environments where users, applications, and data are distributed across offices, cloud platforms, and remote locations.
Common SASE capabilities include:
- SD-WAN: Connects users, offices, and applications.
- ZTNA: Provides controlled, application-level access.
- Secure web gateway (SWG): Inspects and filters web traffic.
- Cloud access security broker (CASB): Controls access to cloud applications.
- Cloud firewall: Applies network security policies through the cloud.
In simple terms, SASE provides the architecture, while Zero Trust provides the security approach for controlling access within that architecture.
Example: a remote employee may need access to a customer management application. Zero Trust principles determine that the employee and device should be verified and that access should be limited to the required application. SASE provides the cloud-based connectivity and security services that help deliver and enforce that access.
Network security compliance and regulations
Network security requirements can come from different types of frameworks, laws, and industry standards. Which ones apply depends on the organization’s industry, location, systems, and the type of information it handles.
The important point is that compliance does not mean using a specific security product. Organizations need to understand which requirements apply to them, identify the controls those requirements call for, and maintain evidence that those controls are operating effectively.
1. NIST Cybersecurity Framework (CSF) 2.0
NIST CSF 2.0 is a voluntary framework that organizations can use to structure and manage cybersecurity risk. It is not a law, but it provides a common approach for organizing security activities across the network and broader technology environment.
The framework is organized around 6 functions:
- Govern: Establish cybersecurity strategy, roles, and accountability.
- Identify: Understand assets, systems, and cybersecurity risks.
- Protect: Apply safeguards such as access controls and secure configurations.
- Detect: Identify suspicious activity and potential security events.
- Respond: Contain and manage cybersecurity incidents.
- Recover: Restore systems and improve security after an incident.
2. ISO/IEC 27001:2022
ISO/IEC 27001 is an international standard for establishing and maintaining an Information Security Management System (ISMS). It is not a cybersecurity law, but organizations can use it to build a structured, risk-based approach to information security.
For network security, relevant controls include:
- Network controls: Protect network infrastructure and communications.
- Security of network services: Define and monitor security requirements for network services.
- Segregation of networks: Separate networks based on security requirements.
- Web filtering: Control access to potentially harmful external websites.
3. PCI DSS 4.0.1
PCI DSS applies to organizations that store, process, or transmit payment card data. Unlike NIST CSF and ISO/IEC 27001, PCI DSS is an industry security standard with specific requirements for protecting the cardholder data environment.
Network-related requirements include:
- Network security controls: Configure and maintain security controls around the cardholder data environment.
- Secure configurations: Prevent insecure default settings and configurations.
- Encryption: Protect payment card data when transmitted across open or public networks.
- Logging and monitoring: Maintain records that support security monitoring and investigation.
- Network segmentation: Where used to reduce the scope of the cardholder data environment, segmentation must be properly implemented and tested.
4. DORA
The Digital Operational Resilience Act (DORA) applies to financial entities operating in the EU and addresses ICT risk and operational resilience. It has applied since January 17, 2025.
Network security forms part of the broader ICT risk management requirements, alongside areas such as:
- ICT security policies and controls
- Incident management and reporting
- Resilience testing
- ICT third-party risk management
- Protection and monitoring of ICT infrastructure
5. NIS2
NIS2 is an EU cybersecurity directive that establishes cybersecurity risk-management requirements for organizations in designated critical and important sectors. Because it is a directive, specific obligations are implemented through national laws in EU member states.
Article 21 includes measures covering areas such as:
- Risk analysis and security policies
- Incident handling
- Business continuity
- Supply chain security
- Access control
- Cryptography
- Cybersecurity training
- Assessing the effectiveness of security measures
6. HIPAA Security Rule
The HIPAA Security Rule applies to US covered entities and business associates handling electronic protected health information (ePHI). It requires appropriate administrative, physical, and technical safeguards to protect that information.
Relevant technical safeguards include:
- Access control
- Audit controls
- Integrity controls
- Person or entity authentication
- Transmission security
Conclusion
Network security has become a broader challenge as organizations move beyond traditional office networks and connect more users, applications, cloud environments, vendors, and connected devices. Protecting the perimeter is still important, but it is no longer enough to understand or control everything happening across a modern network.
A strong network security strategy brings multiple layers together, including traffic filtering, access control, segmentation, threat detection, continuous monitoring, and Zero Trust. These controls also need to support the organization’s incident response and compliance requirements rather than operate as separate security initiatives.
The goal is not to build an environment that assumes attacks can always be prevented. It is to make unauthorized access harder, detect suspicious activity earlier, and limit how far an attacker can move when a control is bypassed.
Need to strengthen your network security strategy? Talk to Terralogic’s cybersecurity experts about assessing your network architecture, identifying security gaps, and building a more resilient security strategy.
Frequently Asked Questions (FAQs)
1. What is network security?
Network security is the practice of protecting networks and the data moving through them from unauthorized access and activity. It uses technologies, processes, and policies to control access, protect information, and keep connected systems available.
2. What are the types of network security?
Common types of network security include next-generation firewalls, IDS/IPS, VPN and secure remote access, Zero Trust and SASE, Network Access Control, Data Loss Prevention, SIEM/XDR, and network segmentation. Organizations typically combine several of these controls because each addresses a different part of the network security environment.
3. Why is network security important?
Network security helps protect systems and data from unauthorized access, disruption, and other network-based threats. It also helps organizations maintain visibility and control as their environments expand across cloud platforms, remote users, third-party connections, and IoT or OT devices.
4. What is Zero Trust network security?
Zero Trust is a security approach that does not automatically trust users or devices based on their network location. Each access request is verified based on factors such as identity, device status, and the resource being requested, while least-privilege access limits what the user or device can reach.
5. What are the main network security threats in 2026?
Key threats include ransomware and lateral movement, DDoS attacks, AI-powered attacks, supply chain and third-party network risks, OT and IoT security risks, and insider threats or credential compromise. These threats can originate both outside and inside the traditional network perimeter.
6. How can organizations improve network security?
Organizations can strengthen network security by maintaining continuous patching, using phishing-resistant MFA, segmenting critical systems, monitoring network activity, controlling third-party access, applying Zero Trust principles, testing incident response plans, and aligning security controls with applicable compliance requirements.